On 19 October, a hijacked GitHub account replaced the downloads of existing OVHcloud CLI releases with a program that steals secrets. OVHcloud's founder said a GitHub setting that locks published releases had not been turned on. So I checked the 2,000 most-starred projects on GitHub (data as of 30 October).
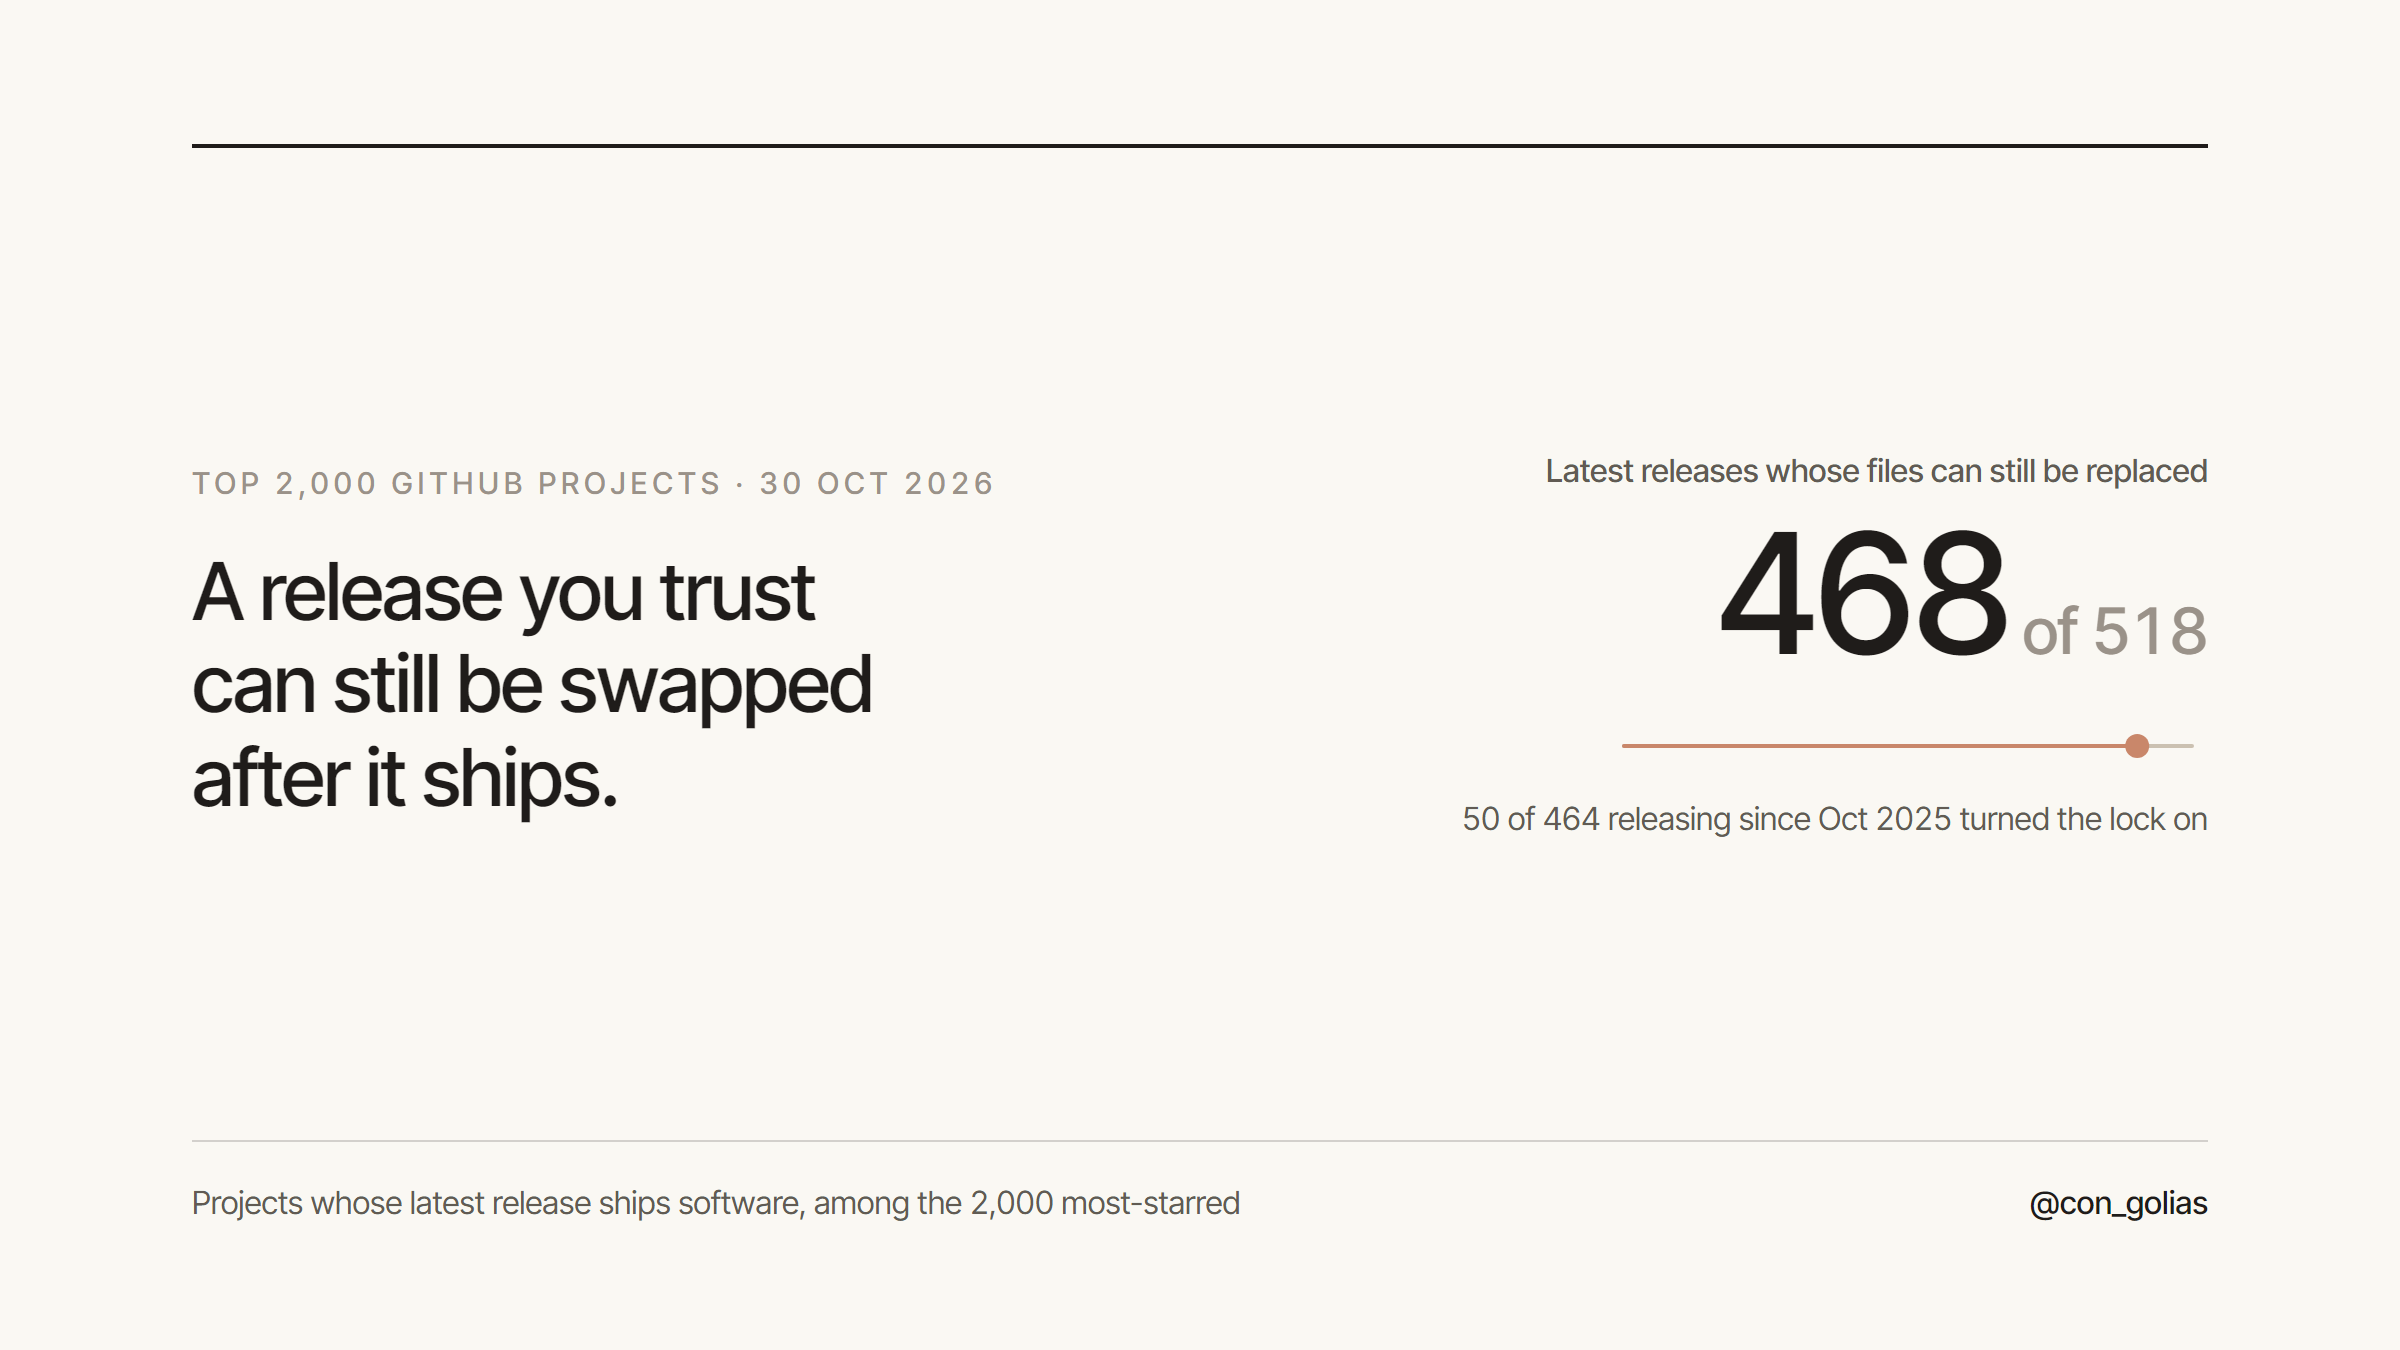
Of the 518 whose latest release ships software, 468 can still have those files replaced the same way.
Of the 464 that have released since the lock became generally available (28 October 2025), 50 published with it on. About one in ten, a year in.
218 of the 518 give a user nothing to check a download against: no lock, no checksum, no signature, no attestation.
The most-starred projects are not noticeably better at it than the rest.
What I took from it as a builder: if a CI step or a Dockerfile downloads a binary from a release page, pin its checksum in your own file. A hash fetched from the same page can be replaced along with the binary. And if you ship binaries, the lock is one checkbox, though it only protects releases published while it is on.
Full method and data in the X Article (30 Oct): https://x.com/con_golias/status/2116214265132564766