I've been building PERMEXIS and PROVE IT v3 under FORGE Defense Technologies. This week, I successfully demonstrated both systems using real security software.
What worked with PERMEXIS:
The live Windows demo blocked unauthorized actions, rejected forged and revoked API keys, enforced destination restrictions, and prevented duplicate execution of repeated requests.
The strongest test was audit integrity. I changed four bytes in a copy of the ledger, turning a DENY into an ALLOW. PERMEXIS detected the tampering immediately and identified the affected record.
What worked with PROVE IT v3:
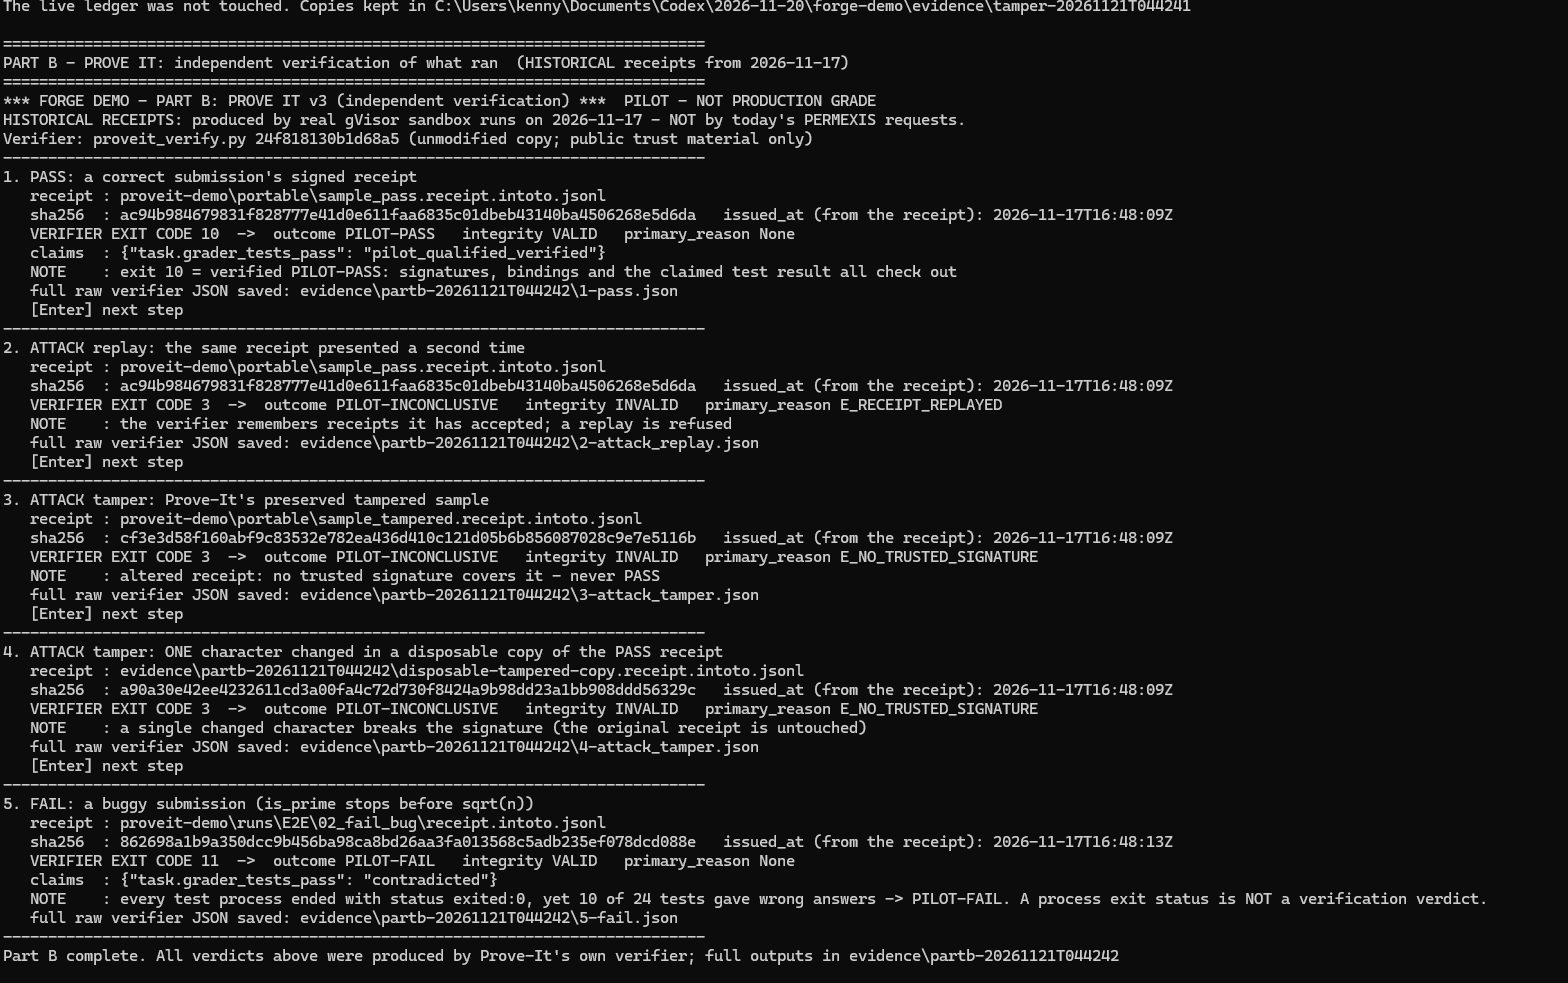
Its real verifier validated signed receipts from previous gVisor sandbox executions, rejected replayed and tampered receipts, and identified incorrect results even when every test process exited successfully.
What I learned:
Authorization and verification solve different problems. Permission to execute doesn't prove an action succeeded, and a successful process exit doesn't establish correctness.
Both demonstrations are repeatable, but they currently run separately. The next milestone is validating the complete live integration.
I'm sharing the progress, limitations, and engineering evidence as I build toward a deployable AI-agent security platform.